Anthropic’s Project Glasswing: Claude Mythos AI Autonomously Uncovers Thousands of Zero-Day Vulnerabilities
On April 7, 2026, Anthropic announced “Project Glasswing” alongside its new frontier model, “Claude Mythos Preview” — which the company describes as “our most capable frontier model to date,” marking a significant leap beyond its predecessor, Opus. While early media reports positioned the model as occupying a new model class above Opus, Anthropic’s official communications have simply characterized it as their highest-performance frontier model to date.
1. 🔐 The Announcement: AI Reshapes the Cybersecurity Landscape
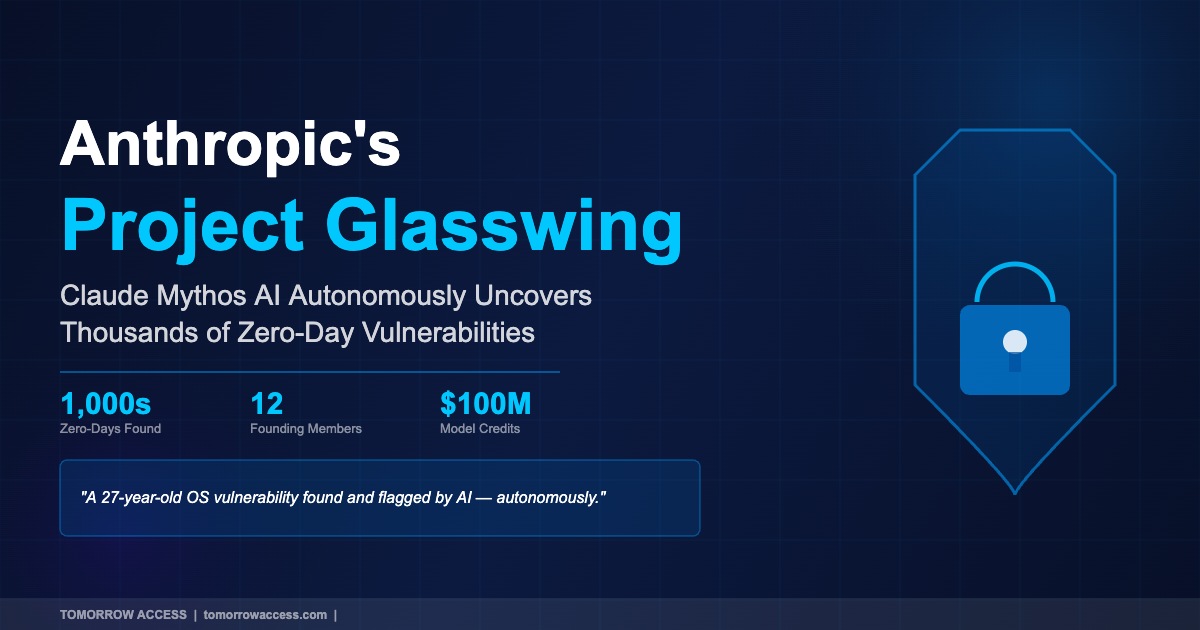
What makes this announcement truly remarkable is Claude Mythos Preview’s ability to autonomously discover thousands of previously unknown zero-day vulnerabilities across major operating systems and web browsers. Among the most striking findings: a flaw that had been silently embedded for 27 years in an OS powering servers around the world — one that, if exploited, could allow an attacker to remotely crash and disable affected infrastructure (now patched).
Even more alarming was a 17-year-old vulnerability found in another widely deployed enterprise OS, which could grant attackers complete remote control — effectively handing them root-level access to the machine. The AI also independently identified a 16-year-old flaw in a multimedia processing tool embedded across countless global services. These were vulnerabilities that human security experts had overlooked for decades. The implication is clear: AI-powered security research has reached — and in some cases surpassed — the capability of the world’s best human specialists.
(Source: Anthropic – Project Glasswing)
2. 🤝 A Coalition of 12 Tech and Financial Giants
Project Glasswing is a restricted-access preview program providing Claude Mythos Preview exclusively for defensive cybersecurity purposes. The 12 founding members are: Amazon Web Services, Anthropic, Apple, Broadcom, Cisco, CrowdStrike, Google, JPMorgan Chase, the Linux Foundation, Microsoft, NVIDIA, and Palo Alto Networks. Beyond the founding cohort, access has since been extended to more than 40 additional organizations that build or maintain critical software infrastructure.
To support the initiative, Anthropic has committed up to $100 million in model usage credits, along with $2.5 million to Alpha-Omega and OpenSSF, channeled through the Linux Foundation and $1.5 million to the Apache Software Foundation — a substantial investment in strengthening the open-source security ecosystem.
(Source: The Hacker News – Anthropic’s Claude Mythos Finds Thousands of Zero-Day Flaws, Simon Willison’s Blog)
3. 🌐 Why Limited Access? The Dual-Use Dilemma
Anthropic’s decision to restrict Claude Mythos Preview to vetted partners is deliberate. A model capable of autonomously discovering and demonstrating zero-day exploits is, by definition, a double-edged sword: in the wrong hands, it becomes a formidable offensive cyberweapon. Anthropic openly acknowledges this paradox — what AI can break, AI can also fix — and is adopting a phased approach, building a defensively-focused security framework before considering broader access.
This development marks a pivotal shift: AI is no longer confined to coding assistance or conversational tasks. It has emerged as a genuine dual-use technology capable of determining the security posture of national and enterprise infrastructure. While efforts like Google’s Project Zero have explored AI-assisted security research, Anthropic’s initiative stands apart in its organizational scale, industry breadth, and the sheer volume of vulnerabilities surfaced.
(Source: Constellation Research – Anthropic launches Project Glasswing)
4. 💼 Key Takeaways for Business Leaders
Project Glasswing carries direct implications for any enterprise navigating today’s threat landscape:
① AI Cybersecurity Is Now a Board-Level Priority
The participation of JPMorgan Chase — one of the world’s most risk-averse financial institutions — signals that AI-powered security has moved from experimental to essential. Organizations that have not yet embedded AI into their security strategy are falling behind.
② Monitor the Emerging Leaders in Defensive AI Security
Consortium members CrowdStrike and Palo Alto Networks are setting the pace in AI-driven security. Startups specializing in AI security — vulnerability detection, zero-day response, SOC automation — are becoming mission-critical partners worth tracking and engaging.
③ Internal AI Security Policy Is a Competitive Differentiator
Now that AI’s ability to autonomously find vulnerabilities is publicly established, enterprises face a new class of risk tied to their own AI deployments. Organizations that move early to define internal governance — covering model access controls, usage boundaries, and sensitive data segregation — will be better positioned for digital trust and regulatory readiness.
Conclusion
Project Glasswing and Claude Mythos Preview mark a clear inflection point: AI has crossed the threshold from productivity tool to strategic defense technology. The AI cybersecurity market is poised for rapid expansion, and the organizations that act now — to understand the landscape, engage the right partners, and establish sound internal policies — will shape the next era of enterprise security.